TPM 2.0 Security Module Hardware Level Encryption Secure Boot System Integrity
$21.30

Features: The TPM 2.0 module delivers hardware security with advanced encryption, decryption, and digital signatures capabilities to safeguards sensitive data from unauthorized access or tampering.
Featuring multi algorithm this TPM security module ensures wide protections while meeting encryption requirements across applications.
Designed for IT professional and enterprises handling sensitive data in finance, healthcare, and government sectors requiring robust device authentication protocols.
Perfect for securing servers, workstations, and IoTs devices during boot processes or data transactions where firmware integrity and cybersecurity compliance are critical.
With standardized TPM 2.0 certification and ABS housing, this compact module integrates effortlessly into existing systems to strengthen endpoints security without compromising performances.Specifications: Item: TPM 2.0 module
Component:ABS.
Size: 26x28mm/1.02x1.1in
Weight: 15gPackage Includes: 1PC TPM2.0 modulenote: Please allow 1-2cm errors due to manual measurement.
Please allow for slight color differences due to different display resolution.
When you click on links to various merchants on this site and make a purchase, this can result in this site earning a commission. Affiliate programs and affiliations include, but are not limited to, the eBay Partner Network.

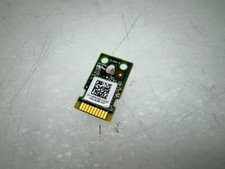 DELL PLATFORM MODULE TPM 1.2 2.0 R640 R740 R440 R540 01MW70 0T2FR2 0CMD3M 0FMYG3$24.99
 Cisco UCSX-TPM2-002 Trusted Platform Module 2.0 for UCS servers 73-17723-06 A0+$34.97
 Cisco UCSX-TPM2-002 Trusted Platform Module 2.0 for UCS M5 Server 73-17723-04 A0$88.07
 TPM2.0 10PIN Security Module Suitable for Supermicro AOM-TPM-9670V-S$13.92
 Cisco UCSX-TPM2-001 Trusted Platform Module 1.2 for UCS servers 73-16747-01 B0+$34.95
 Cisco UCSX-TPM2-002 Trusted Platform Module 2.0 for UCS servers 73-17723-06 A0+$36.99
 2X 42607-0C070 TPMS Tire Pressure Sensors For Toyota Sienna Tundra NEW$28.69
 TPM 2.0 Module 14 -1 Pin MSI$27.56
 www.userbars.org